One console to detect, correlate and respond across SOC, NOC and IT Ops
Your security, network and IT operations teams in one multi-tenant platform, with shared logs, assets and incidents, AI-assisted triage and your choice of SIEM engine. On your premises or in your own cloud.
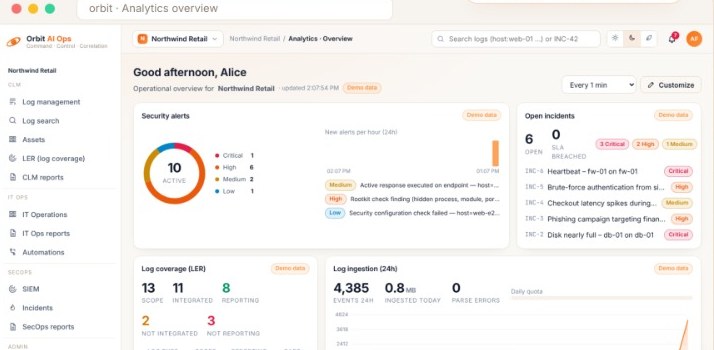
What teams do in Orbit
Central log management
- Log management and parsing
- Log search across tenants
- Asset inventory
- Log coverage: which sources report and which are silent
- Retention, regex search, NAS, SAN and cloud storage
Security operations
- SIEM with built-in detection rules
- Wazuh or Security Onion as the engine
- Incidents with severity, owner and SLA
- Endpoint security: FIM, configuration checks, rootkit checks, active response
- SecOps reports
IT and network operations
- Agent metrics and health
- Auto-discovered assets
- Monitors, services and SLOs
- Automations
- IT Ops reports
Administration
- Multi-tenant organisations
- Role-based access and MFA
- Audit trail
- Integrations and module center
- Agent configuration and updates
Ask in plain language. Approve before anything runs.
Analysts can search logs and investigate incidents by asking questions in natural language. Orbit suggests triage steps and related evidence, and every suggested action is shown for validation before it is carried out.
AI assistance is there to shorten the path from alert to decision. It does not take response actions on its own.
Runs where your data already lives
On-premises
An offline installer that runs as a single container, for networks that cannot reach the internet.
Your cloud account
The same package deployed into your own cloud subscription, under your keys and policies.
Managed service providers
One deployment serving many customers, each in an isolated tenant.
Bring in what you already collect
- EUTA agent
- Syslog / CEF / JSON
- Wazuh
- Security Onion
- REST API
See EUTA and Orbit AI Ops on your use case
A 30-minute walkthrough with our engineers, on sample data, focused on the endpoints and tools you run today.